Your enterprise intranet hosts confidential strategic plans and stores thousands of employee records. It’s one of the most valuable systems in your IT infrastructure. Yet many organizations still rely on a generic security questionnaire, check a few boxes, and hope for the best.
This blind spot is costly. The average data breach now exceeds $4.4 million, according to the IBM Data Breach Report (2025). The financial impact is only one dimension of the fallout. Failed compliance audits halt enterprise sales cycles when prospects demand SOC 2 Type II verification. Regulatory investigations drain resources when auditors discover gaps in GDPR data processing agreements or missing encryption standards.
- Risk assessment and risk treatment
- Asset management
- Access control and identity management
- Cryptography standards
- Physical and environmental security
- Secure software development
- Vendor and third-party risk
- Incident response and business continuity
- Logging, monitoring, and auditability
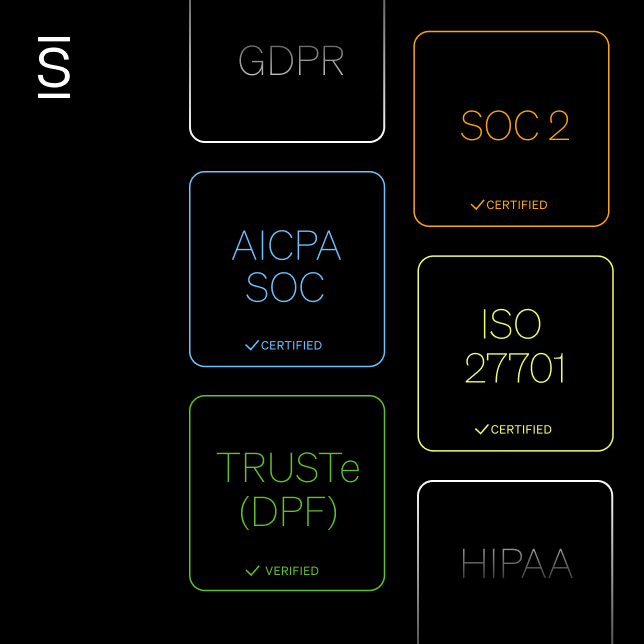
An intranet vendor with ISO 27001 certification has undergone independent audits and adheres to structured, repeatable security processes rather than ad hoc practices.
- TRUSTe Data Privacy Framework (DPF)verification, which requires an audit
- TRUSTe Dispute Resolution
- HIPAA compliance for healthcare
- 23 NYCRR Part 500 readiness for financial services firms
- GXP compliance for the biotech, pharmaceutical, and life sciences fields
This is a partial list. Please contact [email protected] to get the list of other industries or sectors and their specific laws and regulations.
2. ISO 27701 certification
- Defined roles for PII controllers and PII processors
- Policies and procedures for PII collection, use, storage, and deletion
- Processes for data subject rights (access, deletion, correction, consent)
- Privacy risk assessments and mitigation controls
- Vendor and third-party privacy management measures
- Privacy by design/default integrated into systems and processes
While ISO 27001 establishes the foundation for information security management, ISO 27701 ensures your intranet vendor has implemented specific privacy controls required by modern data protection laws. This certification demonstrates that privacy is built into the platform’s design and operations.
- Security: Protection against unauthorized access
- Availability: Uptime, redundancy, failover, and service continuity
- Confidentiality: Controls for restricting information access
- Processing integrity: Accurate, timely, and authorized system processing
- Privacy: How personal data is collected, stored, and used
A Type I report confirms only that controls exist at a point in time, and a Type II audit verifies that the controls actually work over six to 12 months.
- A Data Processing Agreement (DPA) that includes Standard Contractual Clauses (SCCs) for international data transfers
- Built-in tools to track, manage, and fulfill data subject access requests (DSARs) within the 30-day statutory window
- Configurable data retention and deletion policies, including automated purge settings
- Documentation detailing where EU-resident data is stored and processed, including region-specific hosting options
- A transparent list of subprocessors, with their locations and data handling practices clearly documented
- Technical and organizational measures (TOMs) describing how the vendor protects personal data — optional to include, but strongly recommended
Simpplr is fully compliant with GDPR, CCPA, and other legal and regulatory requirements. The platform helps organizations meet their compliance requirements through features such as retention policies, data subject access requests, and standard contractual clauses.
- Complete and publicly accessible list of all subprocessors, including their locations, services, and data-processing responsibilities
- Evidence of each subprocessor’s security posture, such as SOC 2 Type II, ISO 27001, or equivalent certifications
- Data processing agreements (DPAs) with subprocessors that define security requirements, breach notification timelines, and liability terms
- Advance notification of new subprocessors and a documented right to object before they are added
- Documentation that clearly identifies what data each subprocessor can access, the purpose of that access, and how long data is retained
- Regular auditing or monitoring practices the vendor uses to assess subprocessor compliance — optional but very strong
Simpplr partners with more than 20 subprocessors — such as AWS, Apple, Azure OpenAI, Elastic Search, Salesforce, Kaltura, and Google Firebase — to deliver a superior user experience by providing infrastructure, data processing, and storage. These partnerships also possess SOC 2 Type II certifications.
- Transparent privacy policies detailing what information is collected and how it’s used
- Full regulatory compliance with GDPR, CCPA, and other legal requirements
- Real-time access to personal information through web-based interfaces
- Clear contact channels for addressing privacy concerns
Critically, verify that your vendor never sells customer data to third parties for marketing or revenue purposes. This practice, while common in consumer tech, creates unacceptable risk in enterprise environments where proprietary business information flows through the platform daily.
- End-to-end data encryption both in transit and at rest
- Centralized secrets management for storing and rotating decryption keys
- Certified cryptographic modules like FIPS 140-2 Level 3
- Secure algorithms and protocols that mandate TLS 1.2 or above
Simpplr always uses the highest level of encryption available for data in transit (current standard is TLS 1.3) and will only accept connections from clients using TLS 1.2 or higher.
- Real-time vulnerability scanning and threat detection across all system components
- Standardized scoring frameworks aligned with recognized standards such as NIST, ISO 27001, or CIS Controls
Simpplr scored the highest (96 out of 100) on SecurityScorecard among other risk management companies and remains committed to protecting information from threats using reasonable safeguards.
- Multiple data centers across physically separated availability zones, connected by low-latency, high-throughput, redundant networks. Application services, storage, and databases can automatically fail over without disruption.
- Automated backups of the full database instance,enabling full restoration if the primary instance fails.
- Built-in replication that creates read replicas, which receive asynchronous updates from the primary database. If the primary instance fails, Simpplr can promote a read replica to a standalone instance to maintain continuity.
Simpplr backs up all data daily in multiple availability zones on a rotating schedule of incremental and full backups. The saved data is encrypted with a key and is stored in S3 internally (managed service by AWS).
- Single sign-on (SSO) or Identity and Access Management (IAM) to simplify and standardize user authentication (Okta, Azure AD, Ping, etc.)
- Application-layer security controls such as web application firewalls (WAFs), API gateways, and runtime application self-protection (RASP)
- Secure development lifecycle (SDLC) practices, including code reviews, vulnerability testing, and patch management
Simpplr uses multiple layers of defense to resist various types of threats and achieve SOC 2 Type II and ISO 27001 certifications, verified through annual audits.
Trust Simpplr for industry security and compliance
Watch a 5-minute demo
See how the Simpplr employee experience platform connects, engages and empowers your workforce.
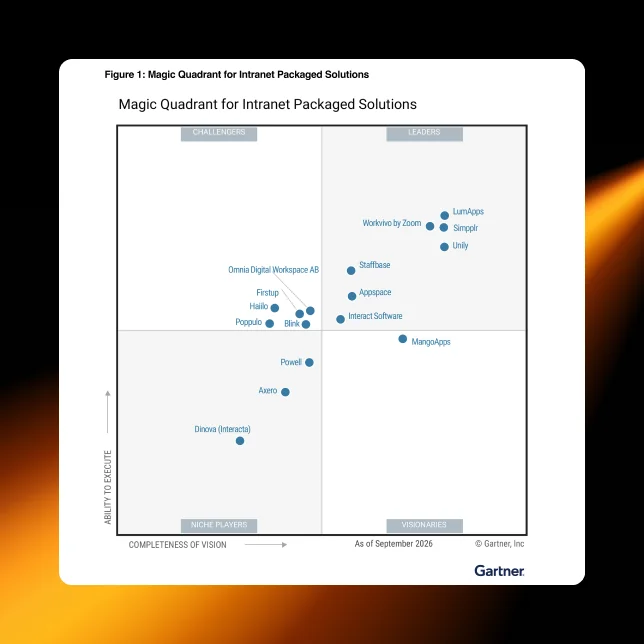
- #1 Leader in the Gartner Magic Quadrant™
- 90%+ Employee adoption rate